Why a Cyberattack Can Resemble a Business
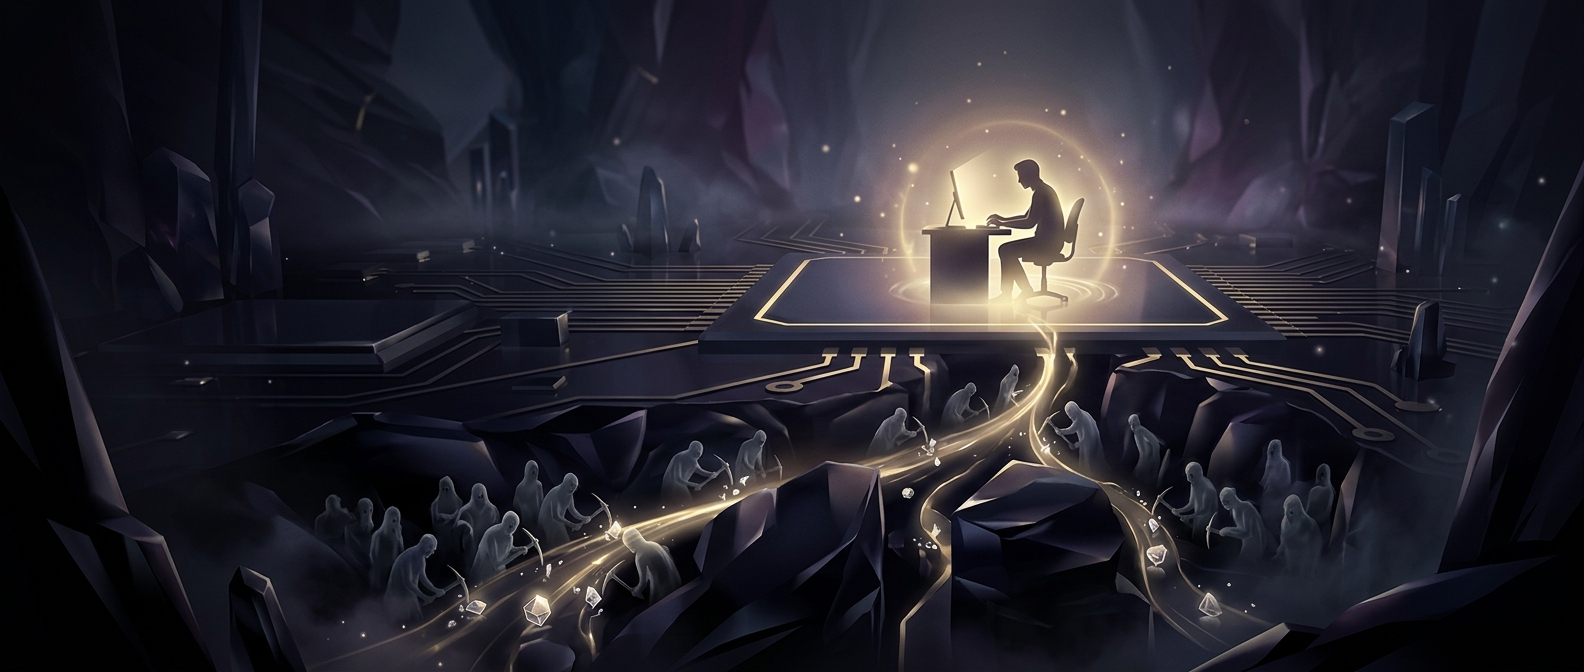
A major intrusion often takes several kinds of work, not one flash of technical brilliance. Someone finds a promising target; others test ways in, maintain access, search for valuable data, or handle the payoff. In criminal operations, those jobs may be divided among separate people or groups. One crew might break into a network and sell access to another that specializes in stealing information or demanding ransom.
That division of labor makes attacks easier to repeat. A group can reuse tools and procedures, track potential victims, and hand work between specialists much as a company passes a project between teams. The spreadsheets and deadlines are not incidental: they help turn a fragile, one-off intrusion into an operation that can pursue many targets.
The Work Behind the Breach
Cyberattacks usually unfold in stages. Attackers may first gather information about an organization or look for a weak point, then try to enter through stolen passwords, deceptive messages, or exposed software. Once inside, they may spend time exploring the network, seeking valuable files or ways to disrupt systems. A breach discovered in a single day can therefore reflect decisions and preparation made much earlier.
Criminal groups also have practical reasons to organize. Ransom demands require communication with victims; stolen access or data can be sold; and specialized expertise can be hired rather than built in-house. These arrangements create costs and risks for the attackers, but they can also let a small core coordinate a much larger operation.
Profit, Power, and Accountability
Not every organized hacking group has the same purpose. Some pursue money, while state-linked operators may seek intelligence, strategic advantage, or disruption. Governments may support teams directly or allow them to operate with varying degrees of official backing, which can make responsibility harder to establish.
For defenders, this changes the problem: stopping one intruder is not always enough if the same access methods, tools, and partners are used again. Security teams must look for patterns across an operation and protect the points where attackers commonly gain a foothold. The cinematic image of one hacker at one keyboard misses the more revealing detail: a breach can be the output of a coordinated process, built to keep working even when individual participants change.