A USB drive can be more than storage
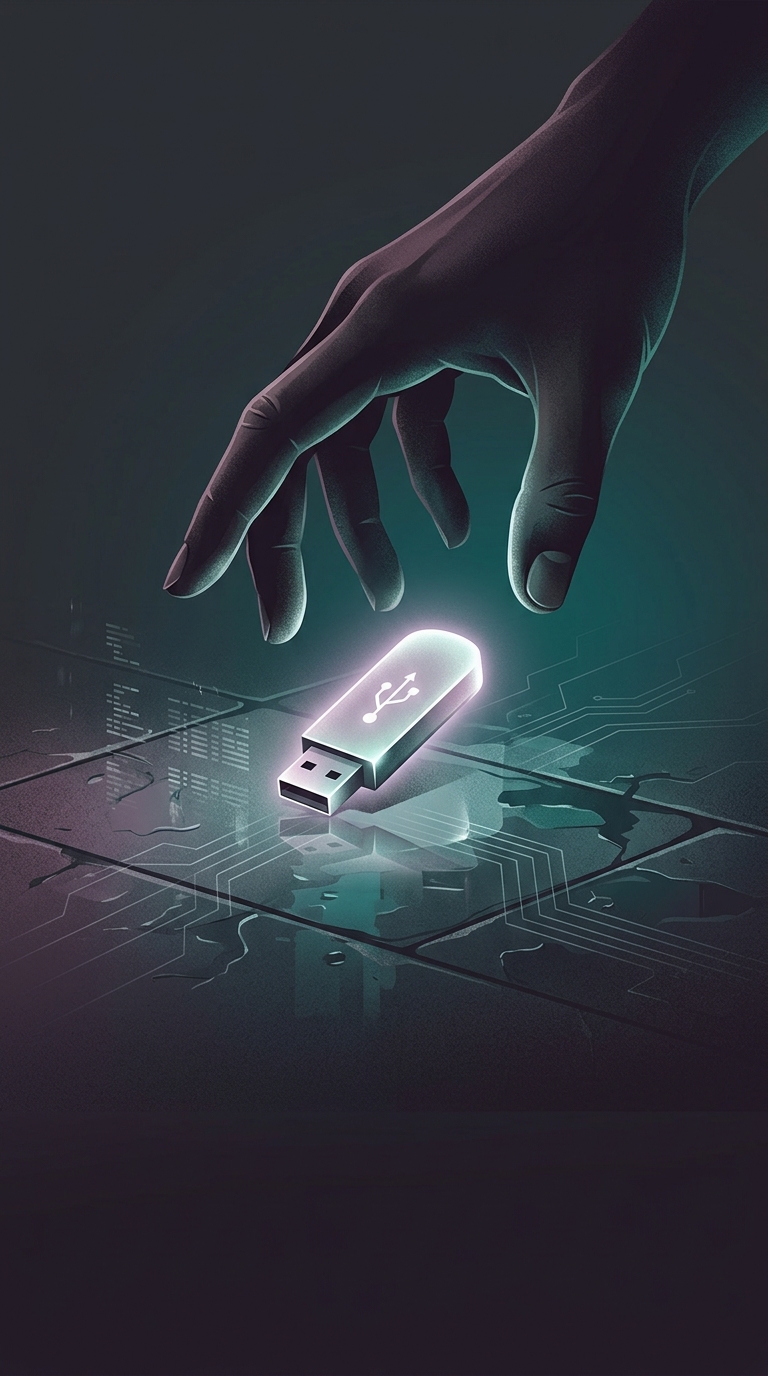
A found flash drive looks like a small, harmless way to move files. But plugging it into a work computer gives an unknown device a direct connection to that machine. The drive may contain malicious files that tempt someone to open or run them; in other cases, the device can pretend to be a keyboard and rapidly enter commands as soon as it is connected.
That second trick exploits trust in the computer’s ordinary input devices. A computer may accept the device as a keyboard without asking whether its commands came from a person. Depending on the machine’s settings and protections, those commands could launch programs, change system settings, or try to download malware. A conventional storage drive is not automatically able to take over every computer, but a user opening a booby-trapped file can still create an opening.
The real target is often the employee
Attackers may leave drives where employees are likely to find them, hoping curiosity or convenience will beat caution. A label such as “Payroll” or “Photos” can make the contents seem relevant. If the device is plugged into a company computer, malware may gain access to work files or accounts, or use that computer as a starting point to probe other systems. What happens next depends on the device, the computer’s defenses, and the permissions of the person using it.
Why security teams say not to plug it in
A found drive has no trustworthy chain of custody: its appearance cannot show what it contains or how it behaves when connected. The safest response is to leave it unplugged and report it to the organization’s IT or security team, which can handle it using isolated equipment if examination is needed. That small pause can prevent a curiosity-driven experiment from turning an unknown object into a path into the company network.