A tiny cost changes the economics of spam
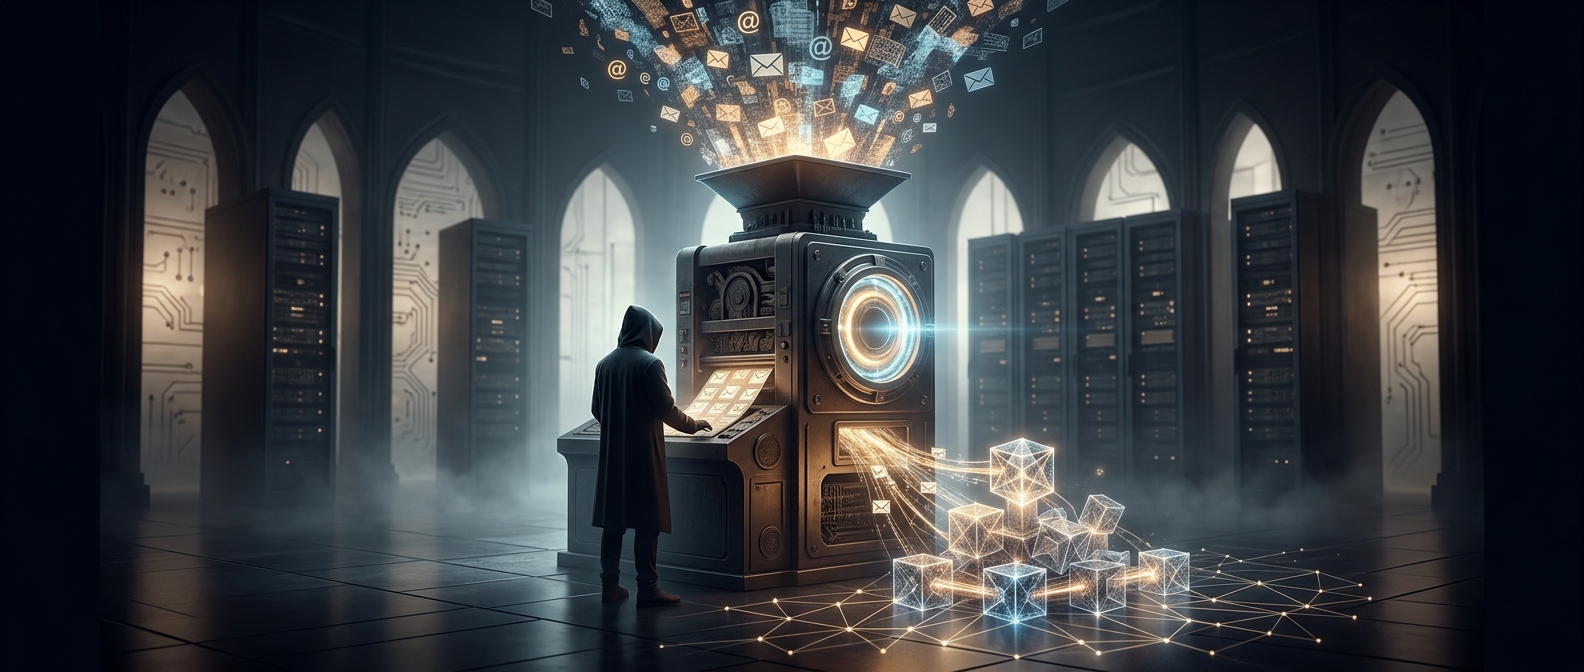
Email is cheap to send, which is convenient for ordinary users and valuable to spammers. A sender can fire off enormous numbers of messages at almost no cost, even if only a few recipients respond. Adam Back’s 1997 Hashcash proposed shifting a small cost onto each message: before sending, a computer would have to find a solution to a puzzle.
The puzzle was designed to be easy to check but require repeated computation to solve. A recipient could quickly verify that a message carried a valid solution. For one email, the work would be barely noticeable; for millions, the repeated effort would consume computing time and electricity. Hashcash did not make spam impossible. It made mass sending less economically attractive by making each attempt cost something.
From email postage to Bitcoin’s shared ledger
Bitcoin adapted that proof-of-work principle for a different job. In Hashcash, the puzzle was attached to an individual message. In Bitcoin, miners compete to find a valid solution for a block of transactions, and the winning block is added to the public ledger. The computation makes it costly to propose blocks repeatedly, while other participants can check a proposed solution much more cheaply.
That cost helps make rewriting the ledger difficult: an attacker trying to replace accepted history would need to redo the work and keep pace with the rest of the network. Bitcoin turned a technique for making unwanted email more expensive into a way to discourage tampering with a shared transaction record. The memorable link is the economic logic: a small cost that barely affects one ordinary action can become a substantial barrier when someone tries to repeat it at scale.