How a fake hotspot gets between you and the internet
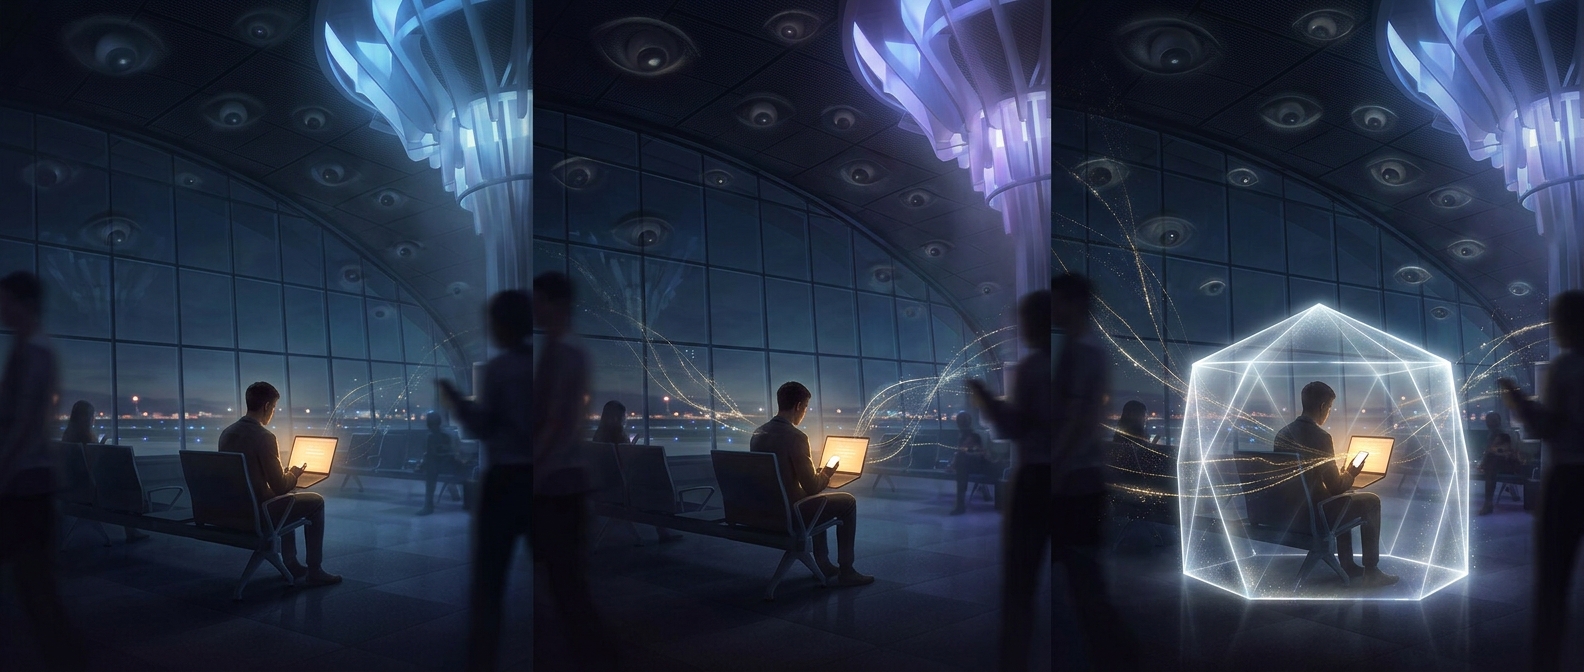
A Wi‑Fi network name is just a label; it does not prove who operates the access point. Someone nearby can broadcast a network with a familiar name, hoping travelers will connect because it looks like the airport’s service. If a device joins, the operator can pass its traffic on to the internet while observing or manipulating parts of the connection. This setup is often called an evil twin.
The danger is not that every message becomes readable. Websites using HTTPS encrypt information between your browser and the site, which generally prevents a hotspot operator from reading passwords or page contents in transit. But a malicious network may still see details such as which online services your device contacts, interfere with connections that are not properly encrypted, or display a counterfeit sign-in page designed to steal credentials. The network can also collect information about the device as it connects.
What protection changes—and what it doesn’t
A VPN, or virtual private network, creates an encrypted tunnel from your device to a VPN provider. That makes it harder for the local hotspot to inspect or alter the traffic inside the tunnel, though it does not make a fake website trustworthy or stop you from entering a password into a convincing imitation page. HTTPS remains important, and unexpected login prompts deserve suspicion.
A personal hotspot uses your phone’s cellular connection instead of the airport’s shared Wi‑Fi, removing the nearby hotspot operator from that route. If you do use public Wi‑Fi, confirm the network name through the airport’s own posted information or staff, and avoid treating a familiar-looking name as proof of authenticity. The key risk is not the word “free”; it is handing your device’s network connection to an access point whose operator you have not verified.