A Small Sensor Can Become a Network Entrance
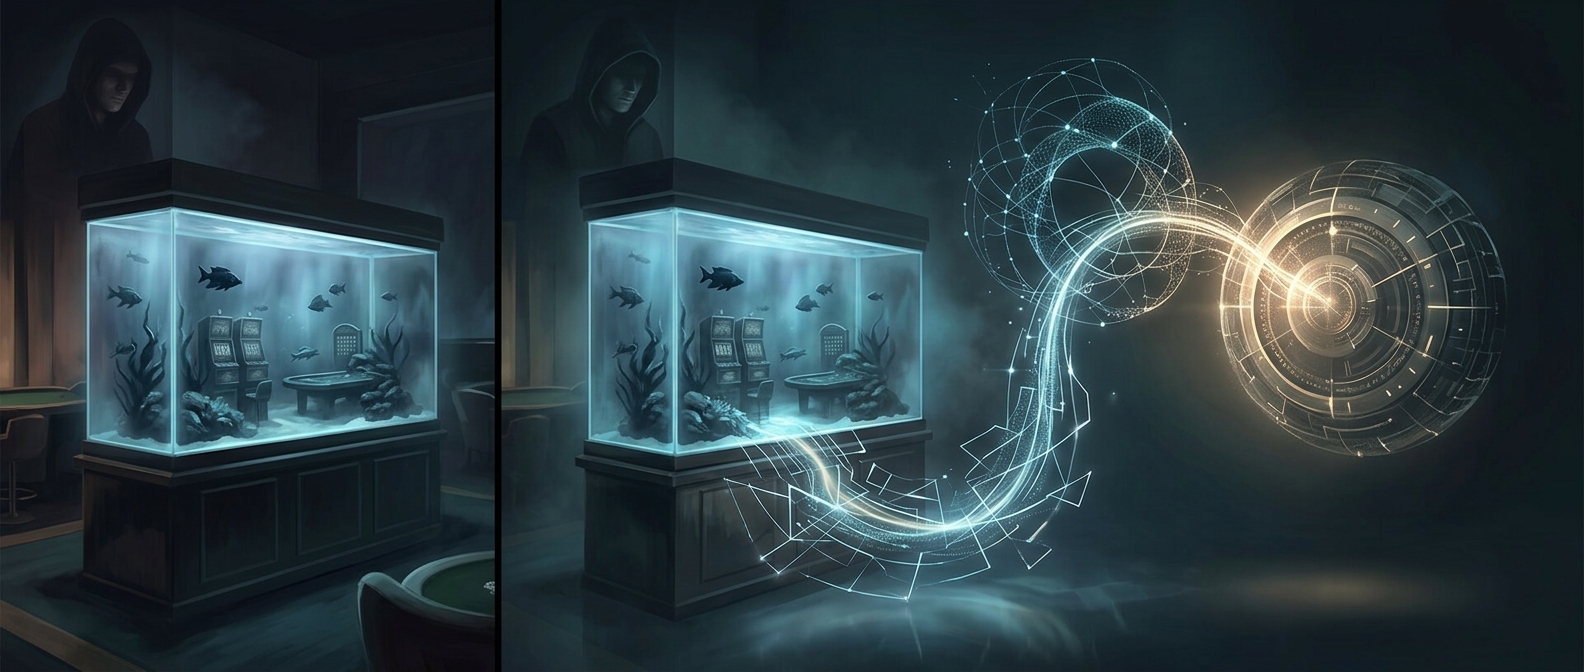
A connected aquarium thermometer is a small computer: it measures temperature and sends readings over a network so staff can monitor the tank without checking it by hand. That convenience also means the device has software, network access, and a potential point of failure. If attackers can compromise it, the important question is not only what the thermometer controls, but what else its connection can reach.
The Risk Was the Route Beyond the Tank
In a well-separated network, a device used to monitor an aquarium would be confined to that narrow task. It might send readings to a monitoring system, but it would not be able to communicate freely with computers holding business or customer information. This separation is called network segmentation: dividing a network into smaller zones and limiting traffic between them.
The casino breach showed what can happen when that boundary is inadequate. After getting into the thermometer’s network connection, attackers used it as a stepping-stone toward other parts of the organization’s network. The sensor did not need to contain valuable information itself; it mattered because it provided a foothold from which attackers could move farther.
Why Connected Gadgets Need Boundaries
Many ordinary devices now connect to business networks—sensors, cameras, printers, and building controls among them. They can be easy to overlook because they are not treated like desktop computers, even though they can still be exposed to software flaws or weak security. Limiting each device to only the systems it needs to contact can keep a compromise from spreading.
The striking lesson is that the aquarium was not the prize. The path out of its thermometer’s network zone was.