A crash put the bomb’s safeguards to the test
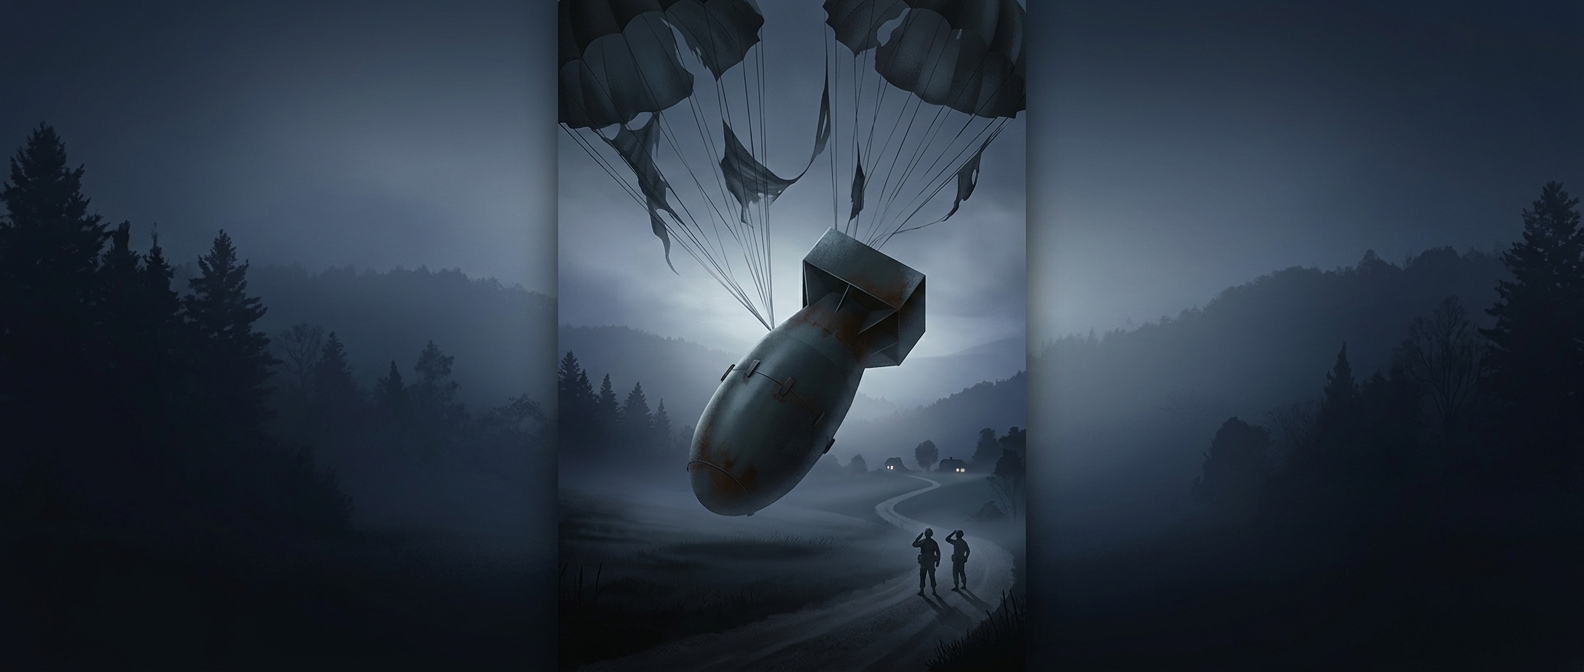
On January 24, 1961, a B-52 carrying two hydrogen bombs broke apart near Goldsboro, North Carolina. The bombs were not simply inert cargo once released: each had an arming sequence meant to prepare it for use. In the wreck, one weapon progressed through several steps in that sequence, making the crash a test of whether its remaining safeguards could keep it from detonating.
The switch that stayed in the safe position
A later Sandia assessment drew attention to a low-voltage switch that remained set to safe. In a weapon’s safety system, a switch like this acts as an interlock: unless it changes state, the sequence cannot proceed to the condition needed for detonation. The crucial point was not that the switch stopped the aircraft from breaking apart or halted every part of the arming process. It was that, after other parts of the system had responded to the disaster, this one barrier still held.
That distinction makes the episode more unsettling than a story of a bomb that simply failed to work. A nuclear weapon is designed to follow a sequence of conditions before it can detonate; the crash supplied some of those conditions by accident. The safe position of one switch mattered because the system still depended on it.
Why one barrier matters
The incident exposed a basic challenge in designing nuclear weapons: safeguards must remain effective even when a weapon experiences events no normal operating procedure intends. A switch can be small, but its role is not. At Goldsboro, the outcome turned on a modest component remaining in the state that kept the sequence from becoming a detonation.